DISCOVERY AT MACHINE SPEED
Probing never rests.
Automated reconnaissance seeks reachable services and reusable opportunities.
Explore ingress controls
NEXT-GENERATION SECURITY APPLIANCE
ESBA combines behavioral intelligence with patent-pending advanced cryptographic technology to help prevent and contain agentic AI attacks, limit unauthorized lateral movement, and restrict outbound connections from compromised or rogue workloads.
Automated systems can look for openings, test access, and move through connected infrastructure at a pace that changes the defender's job. Protecting only the front door is no longer an adequate conversation.
DISCOVERY AT MACHINE SPEED
Automated reconnaissance seeks reachable services and reusable opportunities.
Explore ingress controlsAFTER INITIAL ACCESS
Access to one environment shouldn't silently become permission to traverse another.
Explore internal protectionUNAUTHORIZED CONNECTIONS
Unapproved outbound network paths deserve the same deliberate controls as inbound traffic.
Explore egress control02 / PROTECTION BEYOND THE PERIMETER
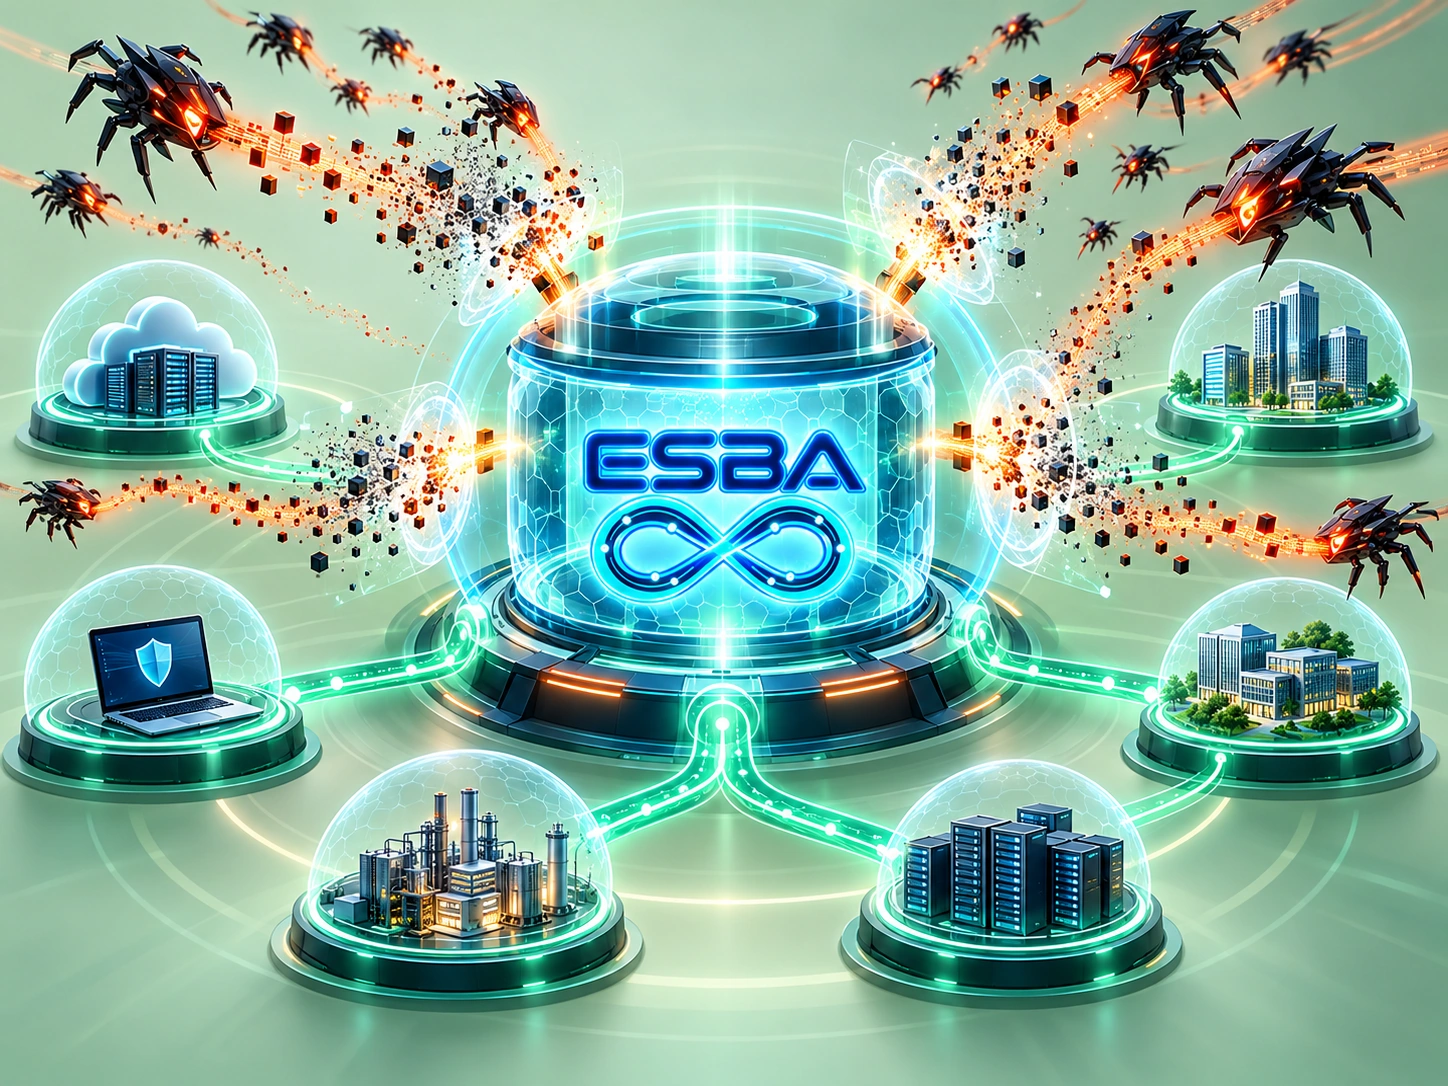
ESBA is placed in the traffic path to apply configured protection at multiple boundaries—not only when a connection first arrives.
Define which inbound TCP and UDP services can initiate new connections. Surface scanning and suspicious probing while permitting explicitly authorized traffic.
Conceptual visualization, not a live traffic display.
03 / WHAT MAKES ESBA DIFFERENT
Security that doesn't assume yesterday's trust should remain standing tomorrow.
ESBA combines configurable inline policy enforcement with a proprietary ephemeral security architecture designed to reduce persistent security context. The underlying cryptographic implementation remains protected intellectual property.
Purpose-bound security context
Defined session lifecycles
Behavioral enforcement layered over core policy
04 / THE APPLIANCE
Purpose-built for real operational work: configure protected environments, set policy boundaries, review enforcement events, and examine what the appliance observes.
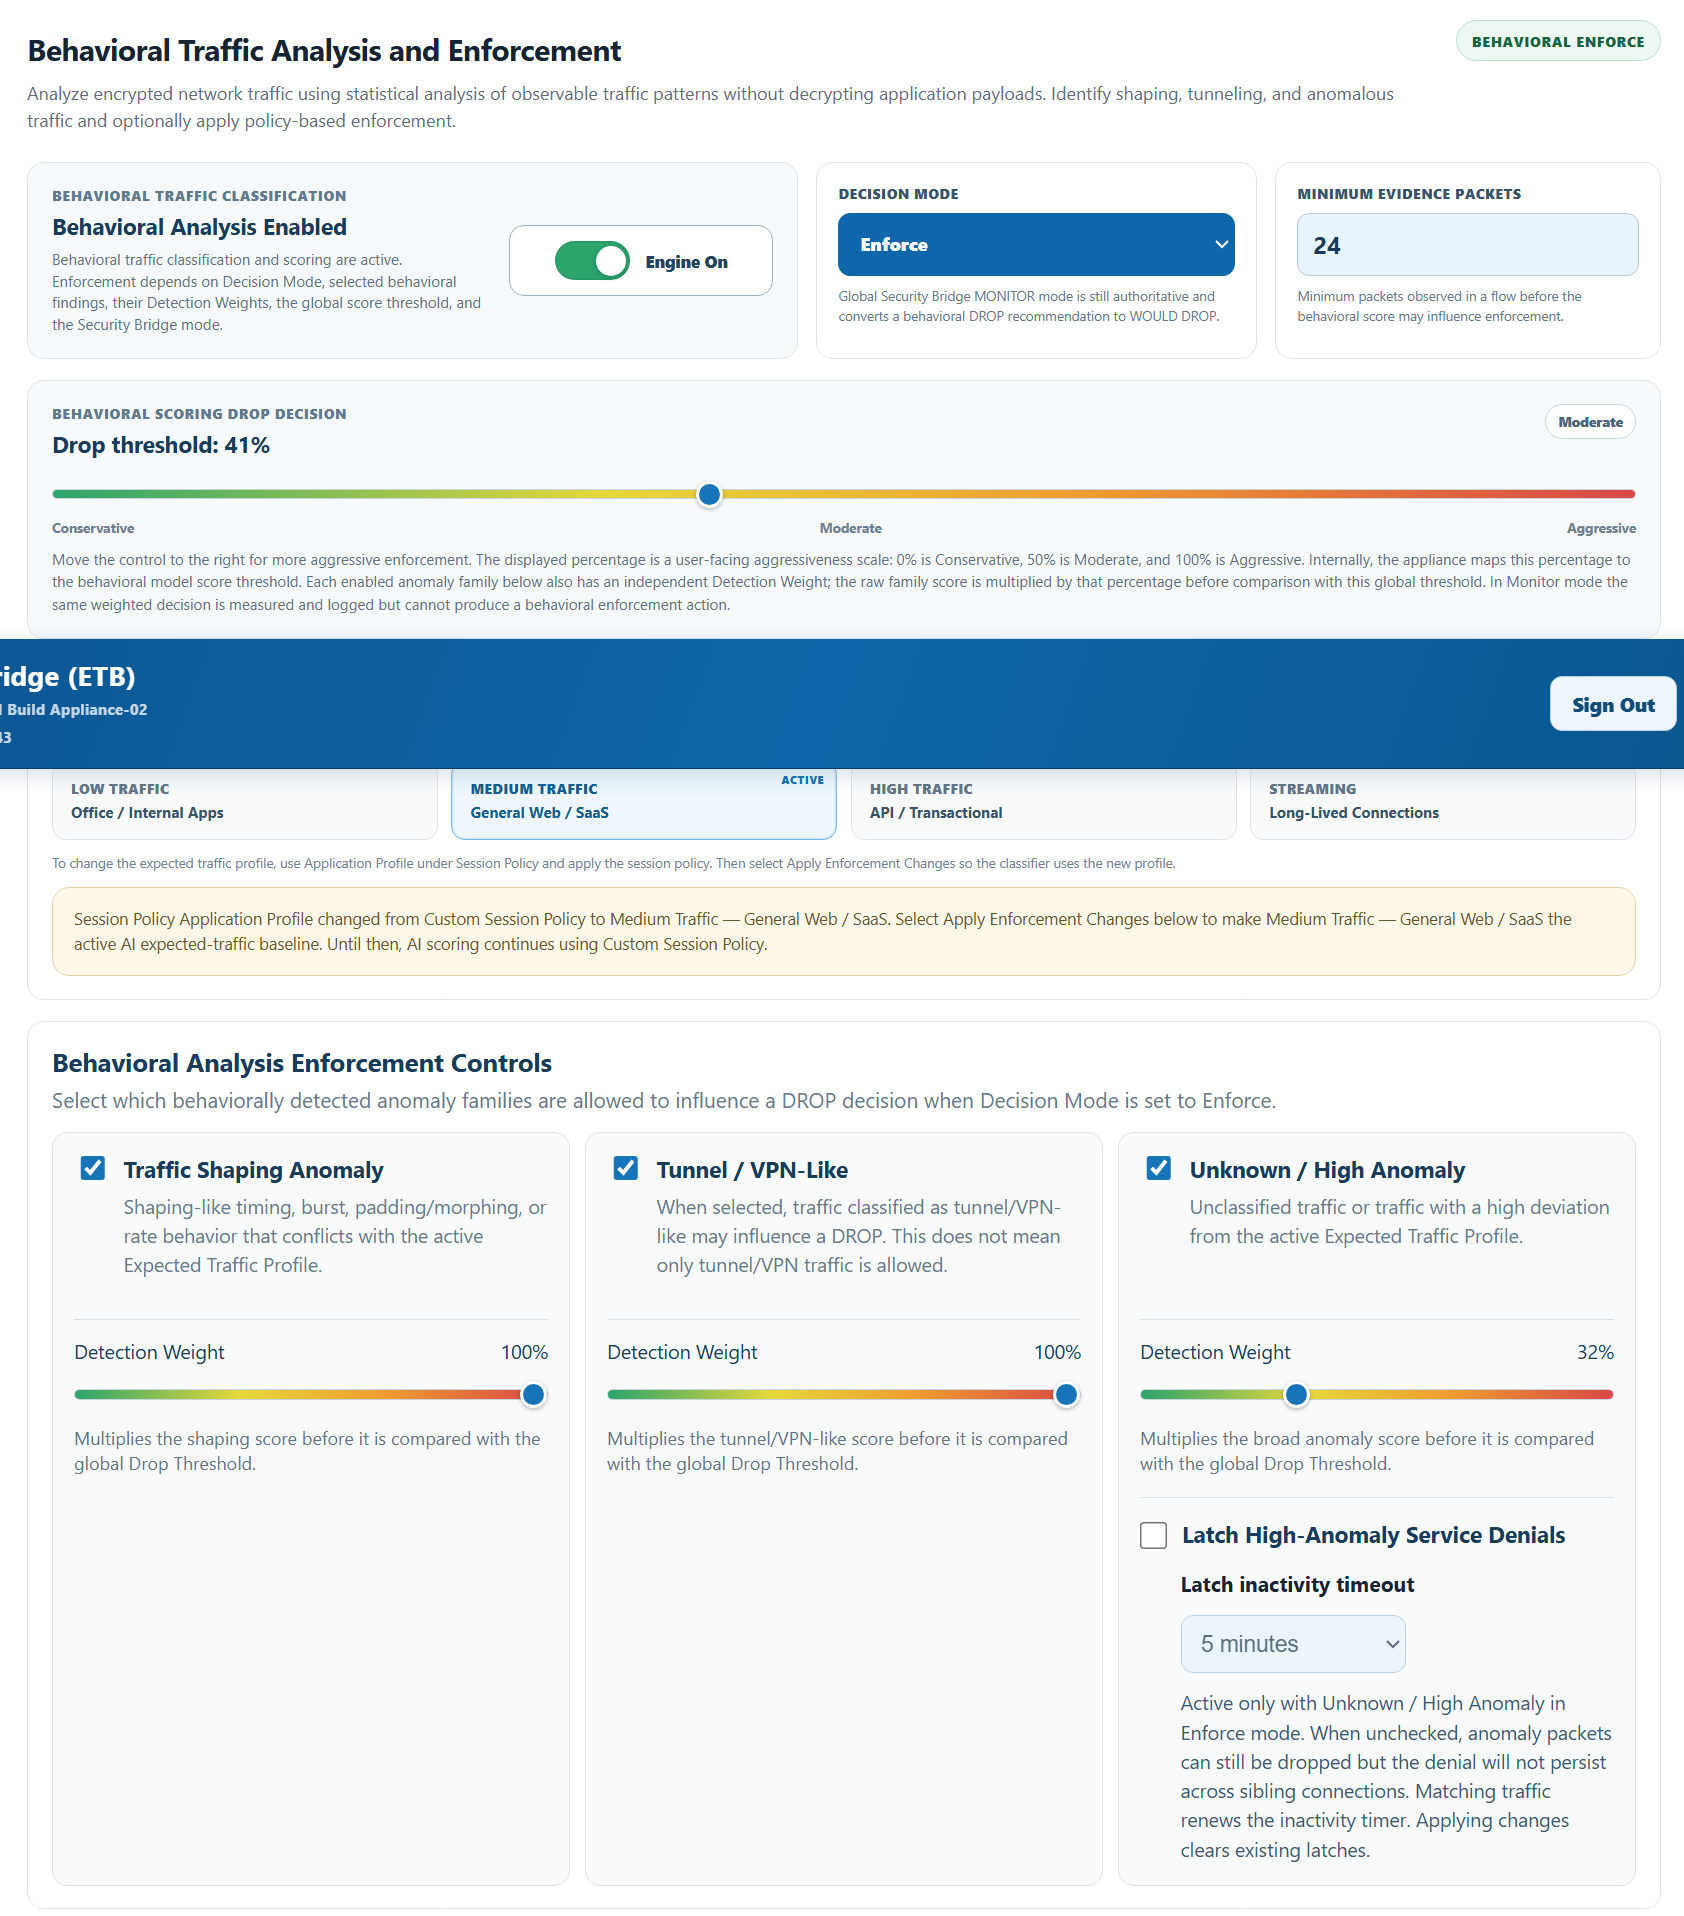
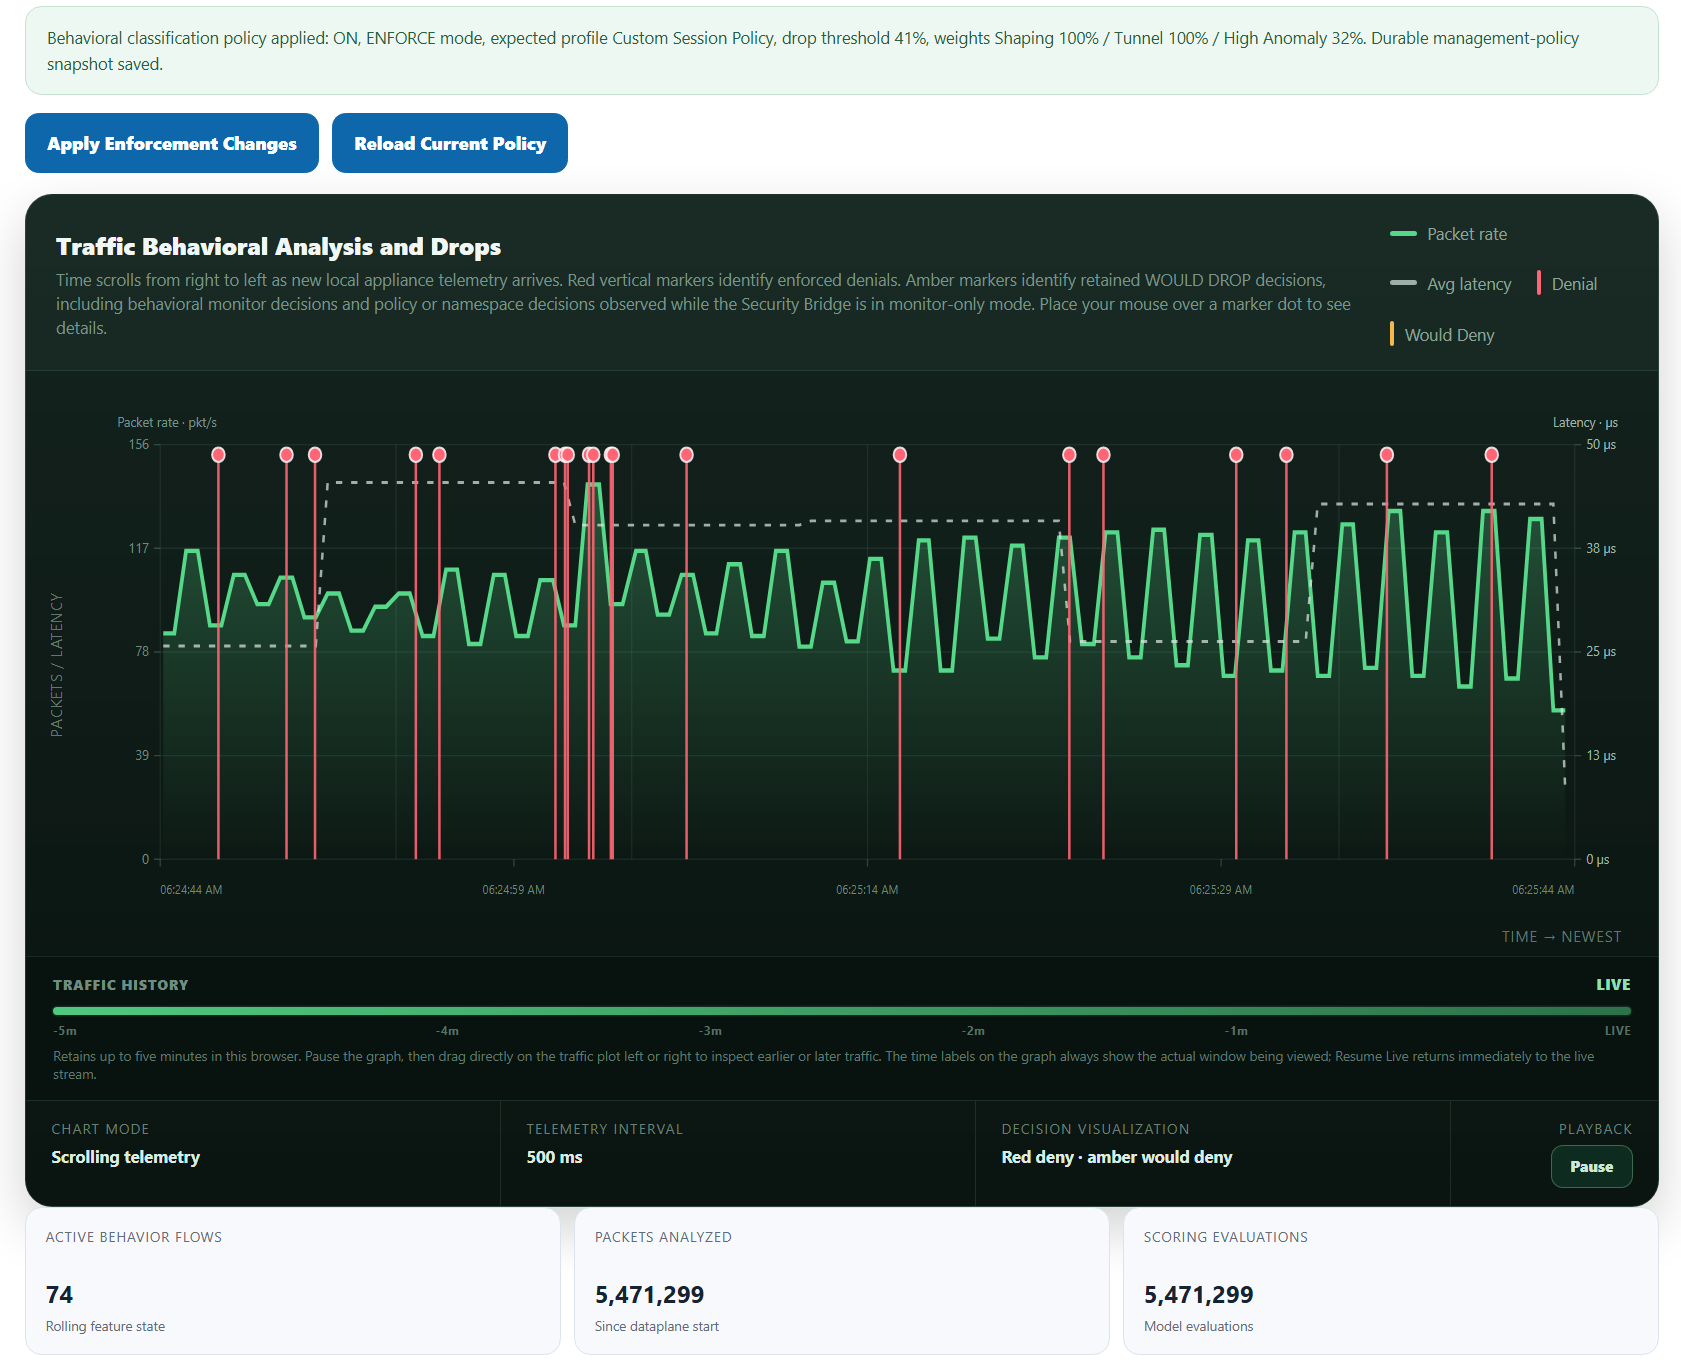
Actual appliance screenshot showing behavioral analysis and enforcement controls.
Configure independent policy for protected networks and traffic relationships.
Identify anomalous patterns and apply configured behavioral enforcement.
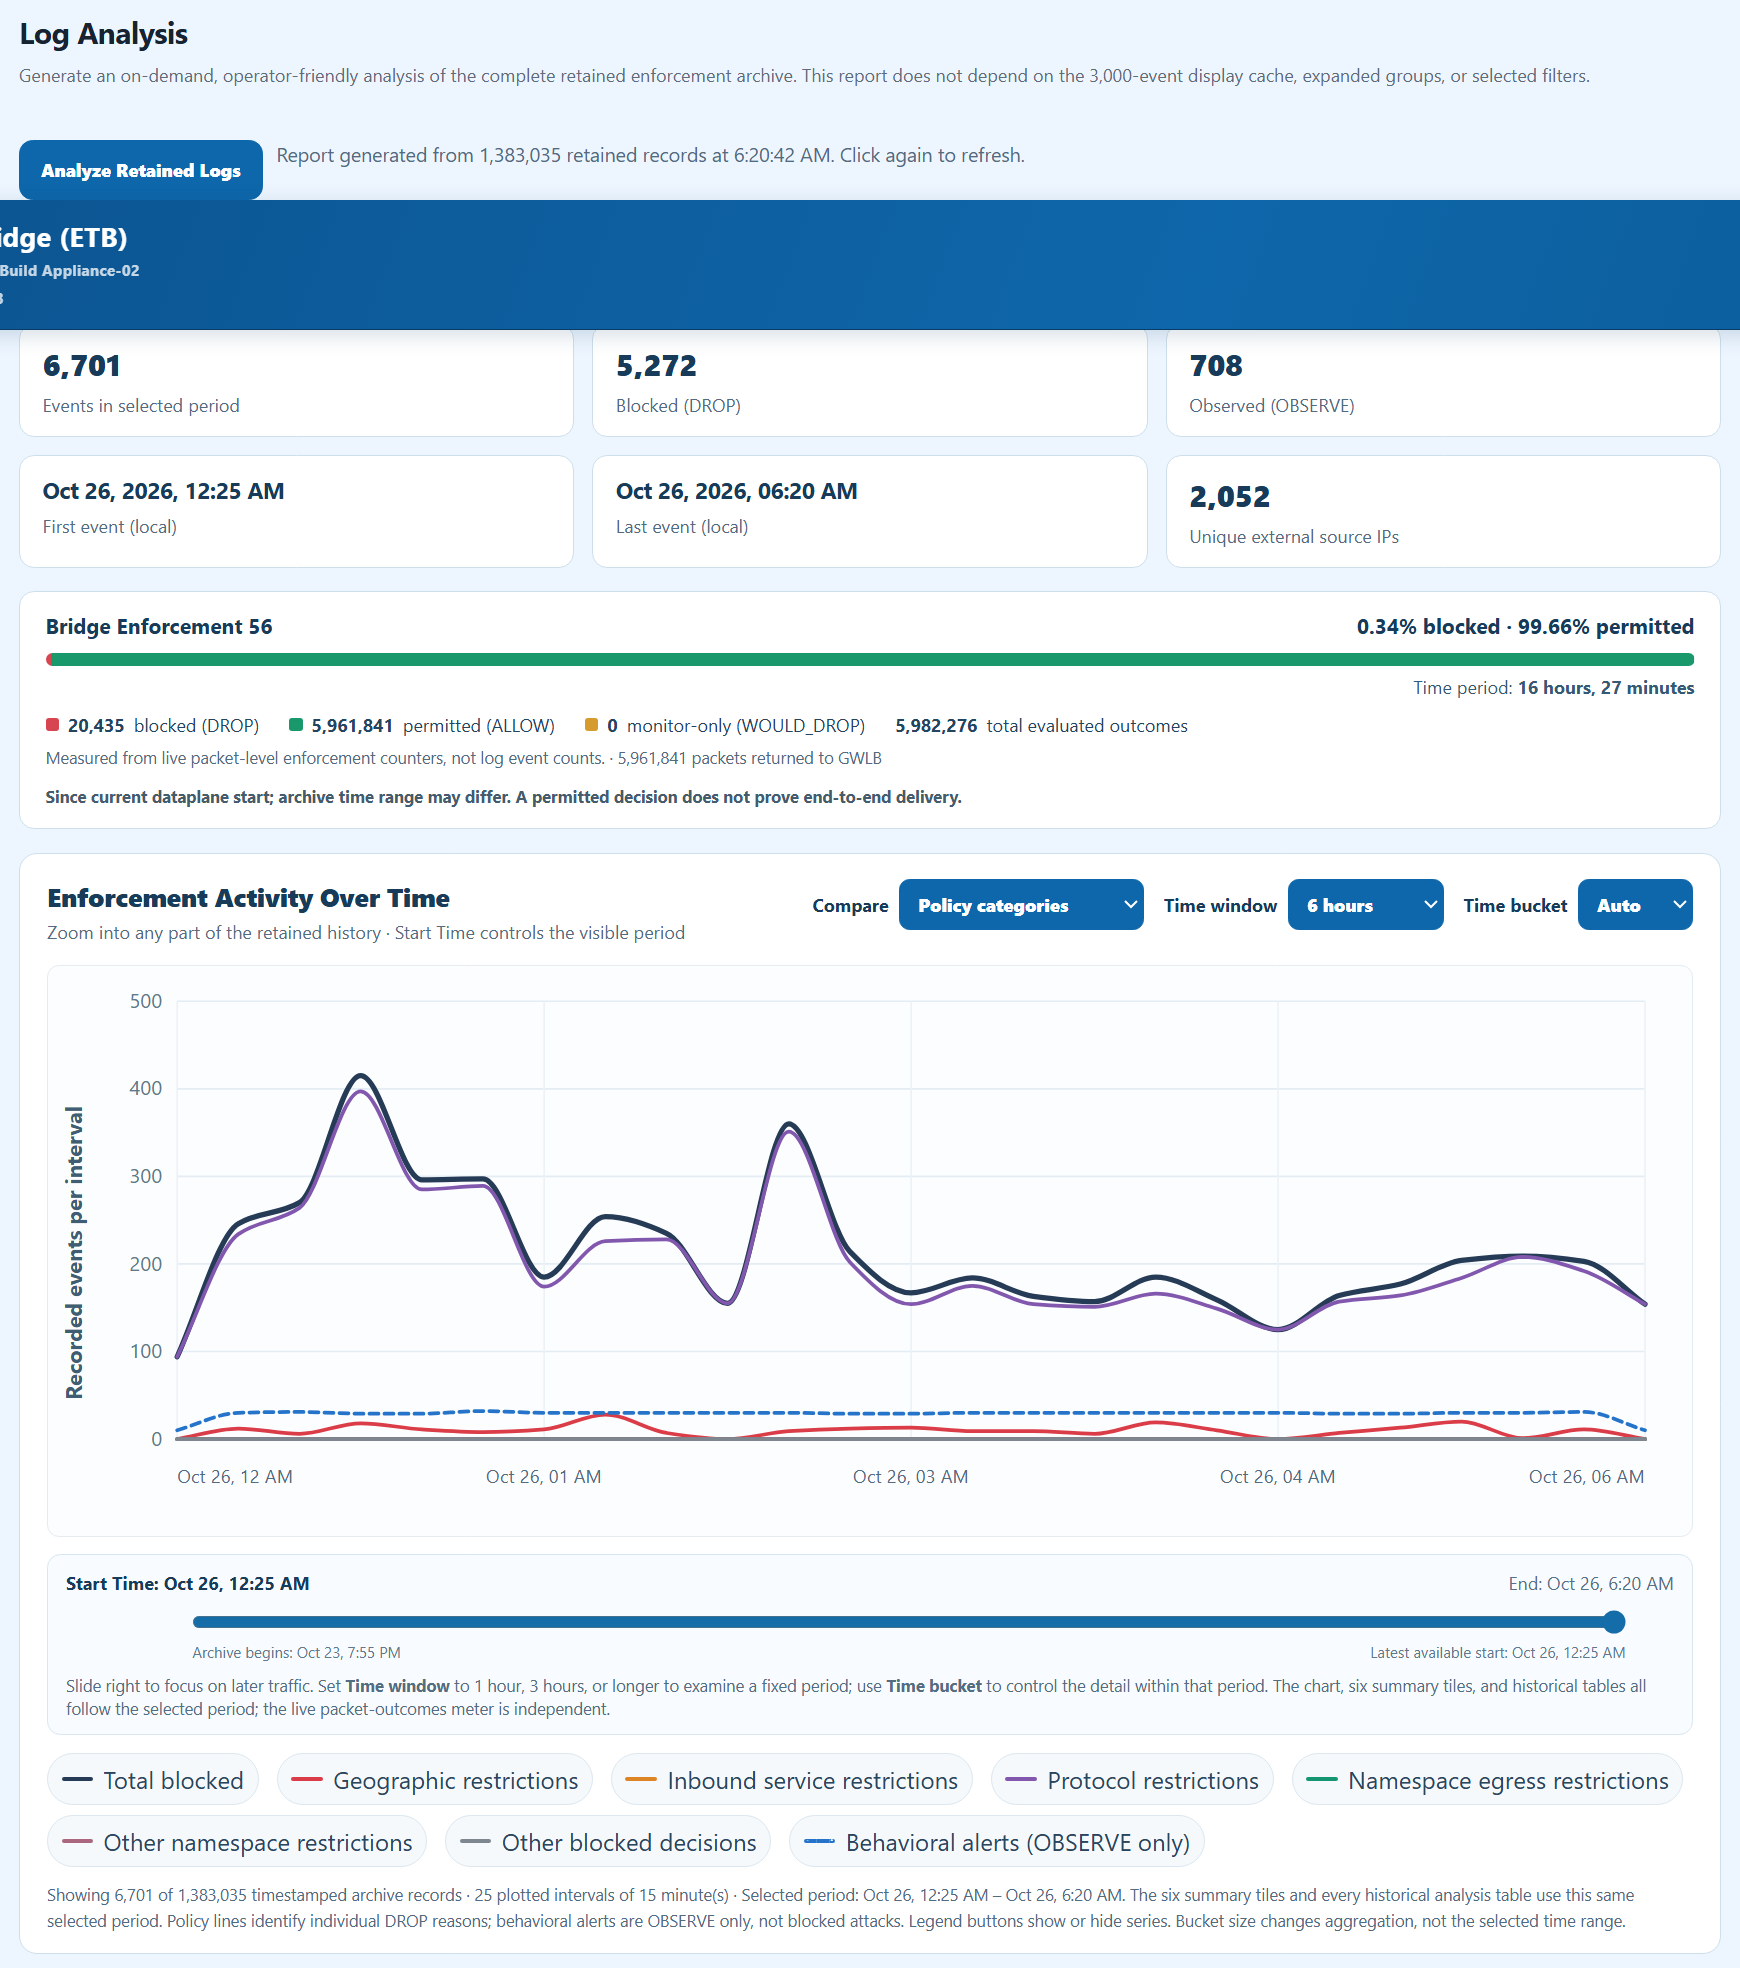
Review enforcement events, session health, lifecycle activity, and telemetry.
An appliance interface designed for day-to-day configuration and review.
The interface shown is an actual ESBA appliance capture, presented as a representative snapshot rather than a live website feed.
ACTUAL APPLIANCE / OPERATOR EXPERIENCE
Actual ESBA appliance interface captures from the engineering pilot. Visuals demonstrate policy enforcement, behavioral telemetry, and retained-log analysis; observations are snapshots, not real-time website statistics.
05 / YOUR ENVIRONMENT, YOUR CHOICE
ESBA operates the appliance infrastructure, with customer-specific protected environments and the same core management and policy capabilities.
Explore hosted deploymentDeploy within your own AWS environment with customer-controlled infrastructure, guided traffic steering, and an appliance management experience.
Explore customer-hosted deploymentBUILT FOR PEOPLE ON THE FRONT LINE
Technology can be sophisticated without making every operating decision a mystery. ESBA puts enforcement controls, meaningful events, and system health into the hands of the teams protecting your infrastructure.
Explore the appliance06 / A CLOSER LOOK
Why security models have to consider how quickly automated activity can probe reachable infrastructure.
Explore the challenge ↗Explore ingress, internal boundaries, and outbound policy as parts of one broader model.
Explore traffic control ↗Why ESBA is built around a proprietary ephemeral approach to security state.
Explore the architecture ↗From namespace policy to telemetry, the appliance connects protection with operator visibility.
Explore the platform ↗QUESTIONS WORTH ASKING
Here are a few useful starting points for an enterprise or technical evaluation.
ESBA is designed to operate alongside existing cloud and network security controls, adding configurable inline policy and ephemeral security capabilities. The appropriate deployment depends on your environment.
It enforces policies on traffic routed through the appliance, including inbound connections, protected-to-protected traffic, and outbound connections where applicable. Traffic routing and namespace policy determine what is in scope.
ESBA includes a behavioral-analysis subsystem that can identify suspicious patterns and apply additional denials when enabled. Core policy remains authoritative; behavioral decisions cannot override a core denial.
Contact ESBA to discuss your environment, deployment model, and whether a technical evaluation or design-partner conversation is appropriate.
Let's talk about protecting your environment with a next-generation inline security appliance.